Claude搓的,直接贴源码以供记录。
#!/usr/bin/env python3
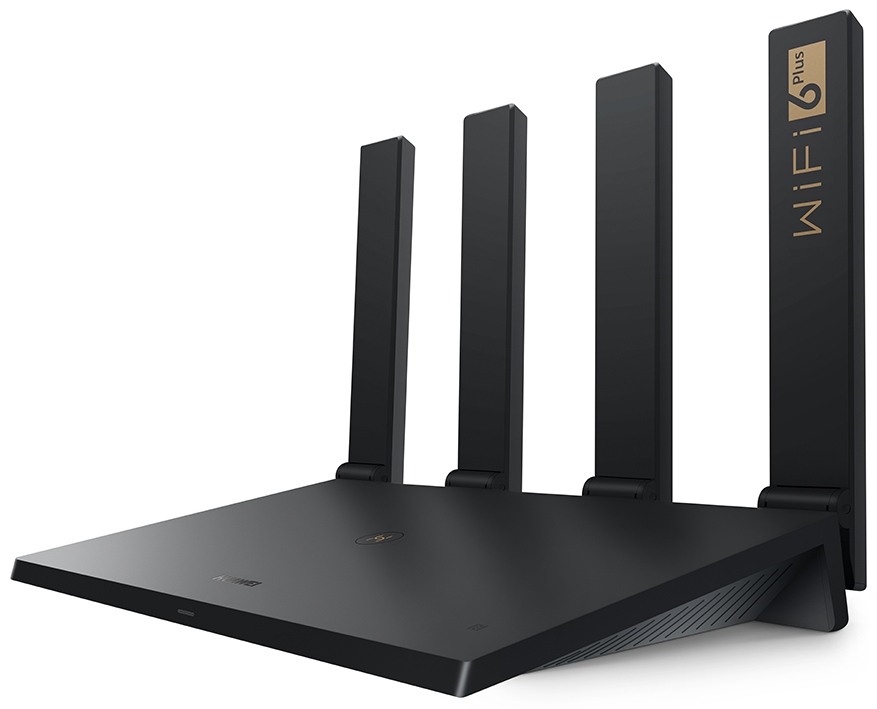
# One-click reboot for Huawei HiLink routers (tested: HUAWEI WiFi AX3 Pro / WS7206-10).
# Login uses Huawei's SCRAM-SHA256 challenge-response.
#
# Usage:
#   hw-reboot --dry-run        # only verify login, do NOT reboot (try this first)
#   hw-reboot                  # log in and reboot
#   HW_PASS=yourpass hw-reboot # pass password via env (otherwise prompts)
#
# Config via env: HW_HOST (default http://192.168.3.1), HW_USER (default admin), HW_PASS
import sys, os, re, json, hmac, hashlib, binascii, getpass
import requests

HOST = os.environ.get("HW_HOST", "http://192.168.3.1")
USER = os.environ.get("HW_USER", "admin")
PASS = os.environ.get("HW_PASS", "pw")
DRY  = "--dry-run" in sys.argv

if not PASS:
    PASS = getpass.getpass("Router password: ")

s = requests.Session()
s.headers.update({"Content-Type": "application/json; charset=UTF-8"})

def die(msg):
    print("FAIL:", msg); sys.exit(1)

# 1) grab initial csrf tokens from the login page
r = s.get(HOST + "/html/index.html", timeout=10)
m1 = re.search(r'name="csrf_param"\s+content="([^"]*)"', r.text)
m2 = re.search(r'name="csrf_token"\s+content="([^"]*)"', r.text)
if not (m1 and m2):
    die("could not read csrf tokens from login page")
csrf_param, csrf_token = m1.group(1), m2.group(1)

# 2) first SCRAM step: send firstnonce
firstnonce = binascii.hexlify(os.urandom(32)).decode()
payload = {"csrf": {"csrf_param": csrf_param, "csrf_token": csrf_token},
           "data": {"username": USER, "firstnonce": firstnonce}}
r = s.post(HOST + "/api/system/user_login_nonce", data=json.dumps(payload), timeout=10)
j = r.json()
if j.get("err"):
    die("login_nonce err=%s" % j.get("err"))
salt, iters, servernonce = j["salt"], int(j["iterations"]), j["servernonce"]
csrf_param = j.get("csrf_param", csrf_param)
csrf_token = j.get("csrf_token", csrf_token)

# 3) compute client proof
salted = hashlib.pbkdf2_hmac("sha256", PASS.encode(), binascii.unhexlify(salt), iters, 32)
# NOTE: Huawei's JS uses CryptoJS.HmacSHA256(message, key) -> key is the 2nd arg.
# So clientKey = HMAC(key="Client Key", msg=saltedPassword), signature = HMAC(key=authMsg, msg=storedKey).
client_key = hmac.new(b"Client Key", salted, hashlib.sha256).digest()
stored_key = hashlib.sha256(client_key).digest()
auth_msg = (firstnonce + "," + servernonce + "," + servernonce).encode()
client_sig = hmac.new(auth_msg, stored_key, hashlib.sha256).digest()
client_proof = binascii.hexlify(bytes(a ^ b for a, b in zip(client_key, client_sig))).decode()

payload = {"csrf": {"csrf_param": csrf_param, "csrf_token": csrf_token},
           "data": {"clientproof": client_proof, "finalnonce": servernonce}}
r = s.post(HOST + "/api/system/user_login_proof", data=json.dumps(payload), timeout=10)
j = r.json()
if j.get("err"):
    die("login_proof err=%s (wrong password, or account locked after retries)" % j.get("err"))
csrf_param = j.get("csrf_param", csrf_param)
csrf_token = j.get("csrf_token", csrf_token)
print("login ok")

if DRY:
    print("DRY-RUN: login succeeded, NOT rebooting.")
    sys.exit(0)

# 4) reboot
payload = {"csrf": {"csrf_param": csrf_param, "csrf_token": csrf_token}}
r = s.post(HOST + "/api/service/reboot.cgi", data=json.dumps(payload), timeout=10)
try:
    j = r.json()
except Exception:
    j = {"raw": r.text[:200]}
if isinstance(j, dict) and j.get("err"):
    die("reboot err=%s" % j.get("err"))
print("reboot sent:", j)
Views: 0